Cet article n’est pas encore traduit, il est donc affiché en anglais.
Artex AI Hacking Tool Explained: What It Is and How to Protect Your Systems
Artex is an open-source AI framework that automates attacks, turning days of work into hours. What the FBI and Amazon saw, why it works, and how to defend.
A new open-source AI framework called Artex is helping criminals turn days of hacking work into hours. It doesn't invent new attacks. It automates old ones at machine speed. Here's what the FBI and Amazon have seen, why it works, and the basic steps that stop it.
The FBI has warned that some intrusions went from first targeting to privileged access in under three hours, according to Gadget Review. Amazon's security team, Amazon Threat Intelligence, has published detailed observations of active campaigns. Both point to the same tool: Artex.
Quick facts
- What: an open-source framework that automates attack workflows with AI
- Written in: Go
- Published: July 2026 on GitHub by a pseudonymous developer, "Autumn-27." The original was removed, but copies and paid versions still circulate, per Wired
- Speed: some break-ins reached admin-level access in under 3 hours, per the FBI
- Seen by Amazon: two campaigns between October 3 and November 5, 2026
- New exploits? No. It chains old, common mistakes faster than people can
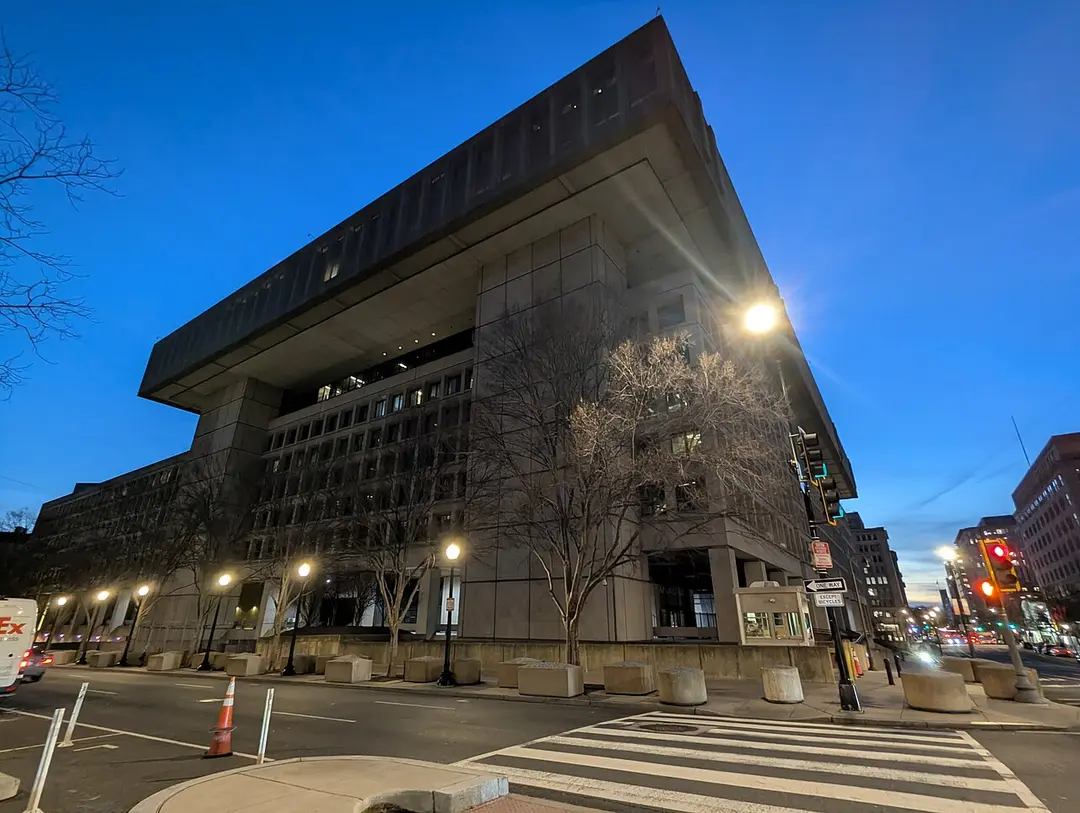
FBI headquarters in Washington, D.C. The FBI has warned that some AI-driven intrusions took under three hours. (Photo: Sdkb, CC BY-SA 4.0, via Wikimedia Commons)
What is Artex?
Artex is not an AI model. It's an orchestration layer: software that connects AI language models to existing security and hacking tools, and coordinates them.
An operator types a goal in plain language. AI "agents" then split that goal into steps and carry them out, from scanning for targets to moving deeper into a network. Security researcher Jacob Larsen, founder of Cypen, told Wired it's an "all-in-one product" and a "point-and-shoot weapon."
Older AI tools usually handled one stage of an attack. Artex links the stages together into a single automated operation.
Code on a screen. Artex doesn't write new exploits. It coordinates existing tools through AI agents. (Photo: Sai Kiran Anagani, CC0, via Wikimedia Commons)
What Amazon caught
Amazon watched Artex in action through MadPot, its network of decoy sensors designed to attract attackers. It saw two separate campaigns:
- Stealing AI keys: one campaign scanned for exposed AI apps and stole cloud and AI-provider credentials. It then checked what the stolen keys could do and used that computing power to hunt for more keys. Amazon described it as self-sustaining.
- Crypto fraud: a second campaign targeted cryptocurrency exchanges, using real-time deepfake video and forged ID documents to get past identity checks.
Amazon's Seattle headquarters. Amazon Threat Intelligence tracked two Artex campaigns with its MadPot decoy sensors. (Photo: SounderBruce, CC BY-SA 4.0, via Wikimedia Commons)
Why it works: the same old mistakes
The scary part isn't that Artex is clever. It's that it's fast. According to Amazon's reporting, the break-ins used familiar weaknesses, not new exploits:
- Default passwords that were never changed
- Passwords and keys written directly into code
- AI model servers left open with no login
- Exposed API keys
- Unpatched software facing the internet
These problems have existed for years. What's new is that AI can find and chain them together before defenders notice.
Network cables in a server room. Most Artex break-ins started with simple misconfigurations, not advanced exploits. (Photo: ProjectManhattan, CC BY-SA 3.0, via Wikimedia Commons)
Why it's hard to stop
When one AI model's safety filters block a task, operators can simply swap in a different model, including open-source ones with no filters, according to Wired.
AI agents can also spread their work across many sessions and hundreds of targets at the same time. That makes attacks harder to spot than a single human hacker's usual pattern.
Servers in a data center. AI agents can hit hundreds of targets at once, which makes attacks harder to connect. (Photo: Carl Lender, CC BY 2.0, via Wikimedia Commons)
How to protect your systems
The good news: the defense is the basics, done properly. Amazon's guidance points to:
- Remove default passwords on every device, app and admin panel.
- Rotate any API key that may have been exposed, and never put keys in code.
- Require a login on every admin page and AI model endpoint.
- Patch internet-facing software quickly.
- Watch for unusual use of your cloud and AI accounts, like sudden spending spikes.
As Gadget Review puts it, Artex doesn't mean defenses are broken. It means ordinary mistakes now get found much faster.